Dallas, Texas, USA
0
Follow on
SCOUT • SECURITY OPERATIONS FOR SMALL TEAMS

Five analysts. Hundreds of alerts. One place to work them.


SCOUT reads every alert, shows its reasoning, and sends what matters to a person. AI does the legwork. People keep the decisions.

Reasoning you can read

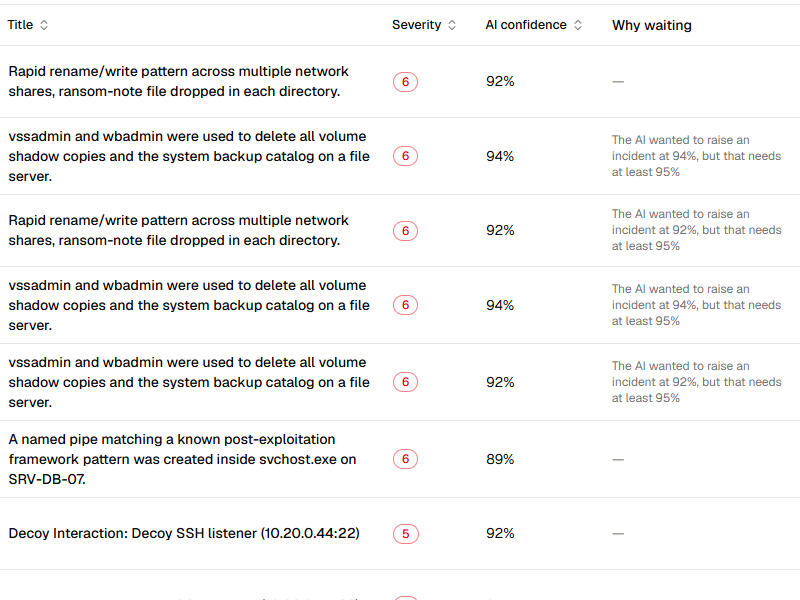
Every AI decision shows what it thought, how sure it was and why.

Approvals that mean something

Risky changes can need a second person, and nobody approves their own.

A record of every decision

Search the audit trail by alert, case or incident number.

Your data stays yours

Run the AI on your own hardware if it can’t leave your network.

THE PROBLEM

Small teams get the same alerts as the big ones

A team of five sees what a team of fifty sees, spread across several tools that don’t share context. The alert is in one place, the case in another, and the lessons learned rarely get written at all.

SCOUT puts the whole job in one place, from the first alert to the review that closes it.

HOW IT WORKS

From the first alert to the lessons learned.

The same path the full tour follows, one Tuesday at a fictional freight company.

AI works the queue and explains each call. Routine items are handled. Anything uncertain waits for a person.
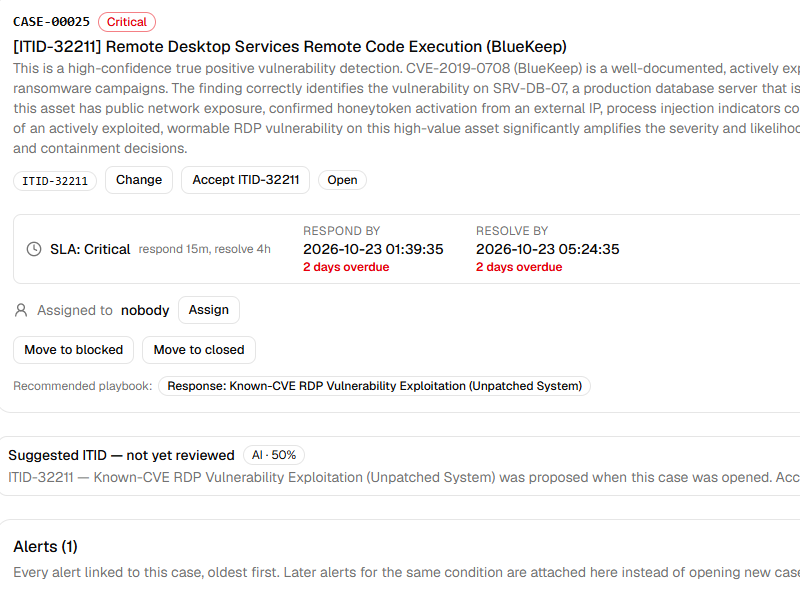
Related alerts become one case with a clock, and you follow the trail.
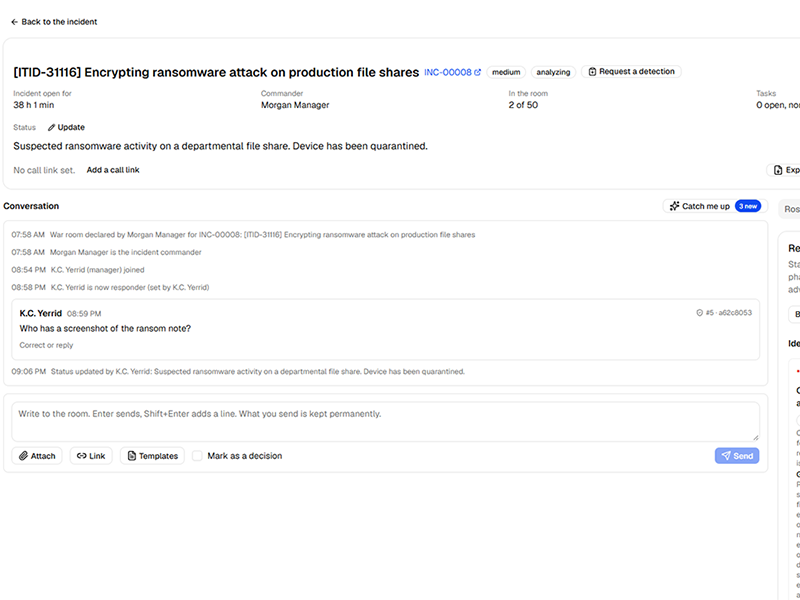
An incident runs with a playbook and a war room that keeps one record.
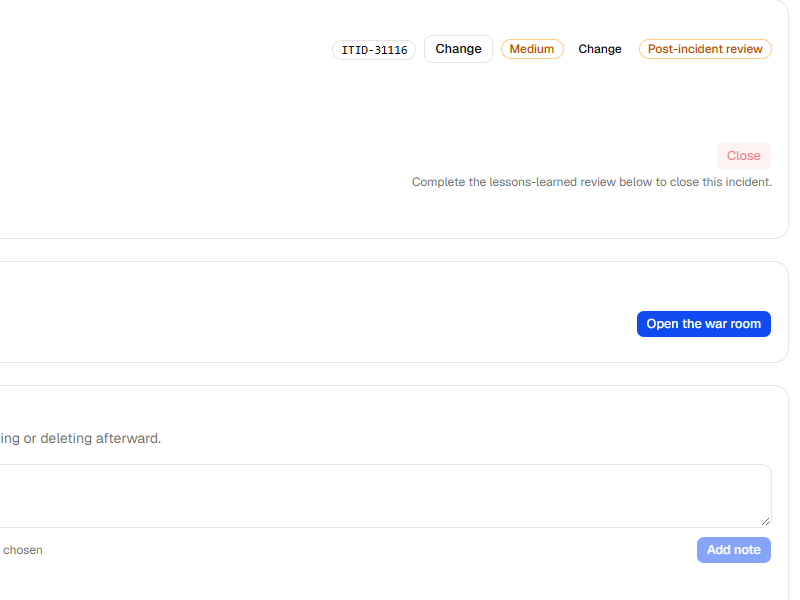
An incident can't close until the lessons-learned review is written.
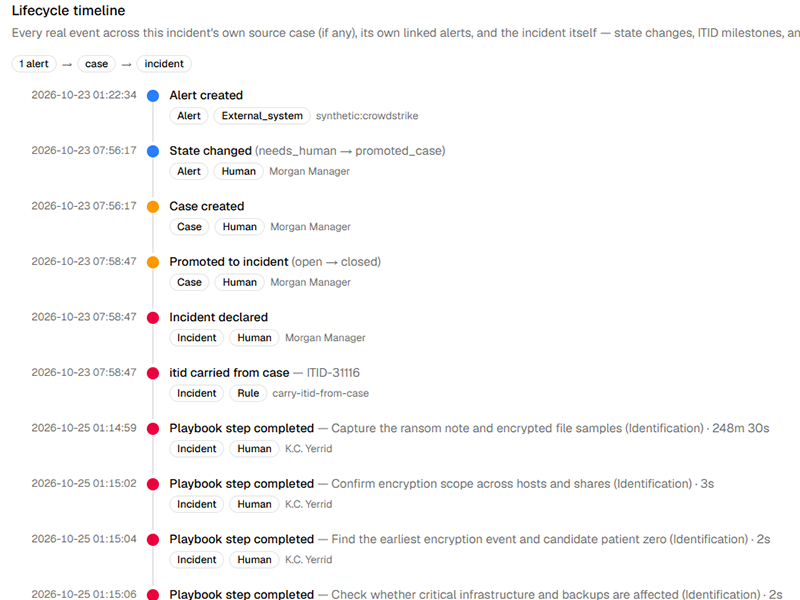
Approvals, limits on the AI and a searchable record of who decided what.
KNOW YOUR EXPOSURE

See what applies to you, and where you're blind.

Image link

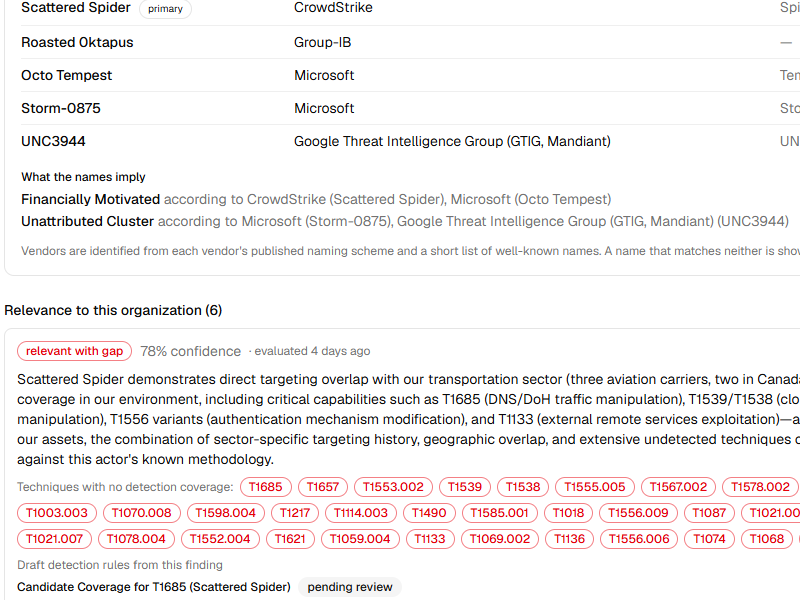
Threat intelligence that knows who you are

SCOUT checks whether a threat actor targets your sector, and shows the techniques it uses that you can’t yet detect.

Image link

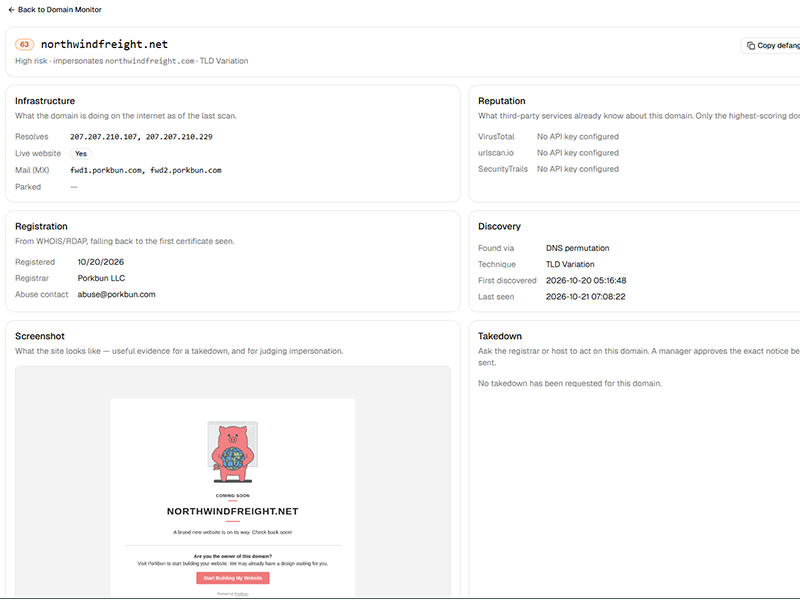
Look-alike domains and exploited vulnerabilities

It watches for sites that impersonate your brand, and for vulnerabilities attackers are already using.

CONTROL AND PROOF

The AI works inside limits you set.

Executives ask the same question: can we explain what it did? Yes, and you decide how much it may do on its own.

You set the limits

A master switch turns the AI’s decisions off entirely. You choose how confident it must be before it acts, and the bar can only go up automatically, never down.

Every decision on the record

Each AI decision is stored with its reasoning. Search it by alert, case or incident number.

Run it on your own hardware

If your data can’t leave your network, SCOUT can use a model you host yourself.

Image link

PEOPLE

Look after the people behind the screen.

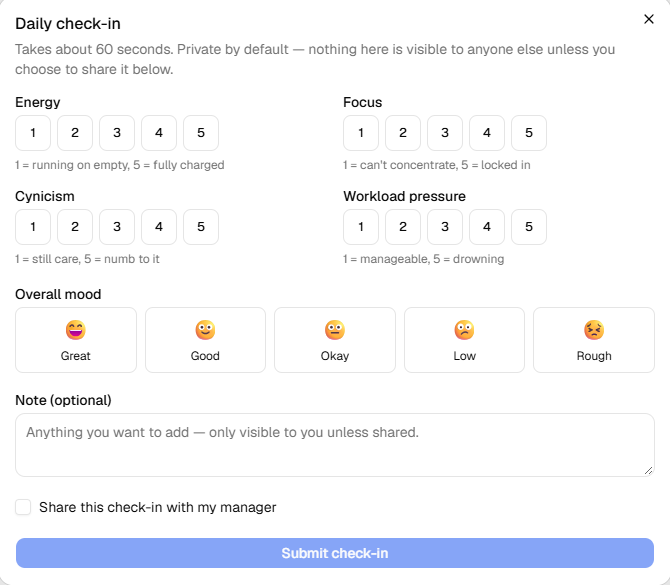
Analysts get a private check-in and a personal trend that only they can see. Managers see team-level results, and an individual’s check-in only when that person chooses to share it.

WHO'S IT FOR

What it does for your team.

Analyst

Manager

Executive

COMPARED

A stack of tools, or one place.

WorkflowA stack of separate toolsSCOUT
Alert triageA queue in each toolOne queue, with the AI's reasoning on every alert
Alert to incidentDetails copied between systemsAlerts become a case, then an incident, in one record
Closing an incidentThe write-up is optionalClosing requires the lessons-learned review
Threat intelligenceRead first, guess relevance laterChecked against your sector, with detection gaps shown
Proving what happenedPieced together from logsA searchable audit trail
Limits on the AIWhatever the vendor choseSet by you, with a master switch

QUESTIONS

What people ask first.

Where does my data go?

By default, alert text goes to the AI service you configure. If that isn’t acceptable, SCOUT can use a model you run yourself, so nothing leaves your network.

Only within the limits you set, and only for actions you’ve allowed. A master switch turns it off, and anything uncertain goes to a person.

You host it on a server you control, in containers (SaaS option is available).

No. The tour uses a fictional company and simulated alerts.

SCOUT is built by Webelo Solutions, a Dallas company focused on leveling the playing field for small and mid-sized businesses. Our founder, K.C. Yerrid, has 30 years of hands-on information security experience, working with security teams of every size. We built it for small security teams because attackers don’t care how big your security team is or how much you spend.

See it with your own data.

A 30-minute conversation. We’ll show SCOUT against a sample of your alerts and answer questions.